
North Korean Hackers Suspected in Record $6.3 Billion Binance Heist as Billions Vanish in Just 20 Minutes
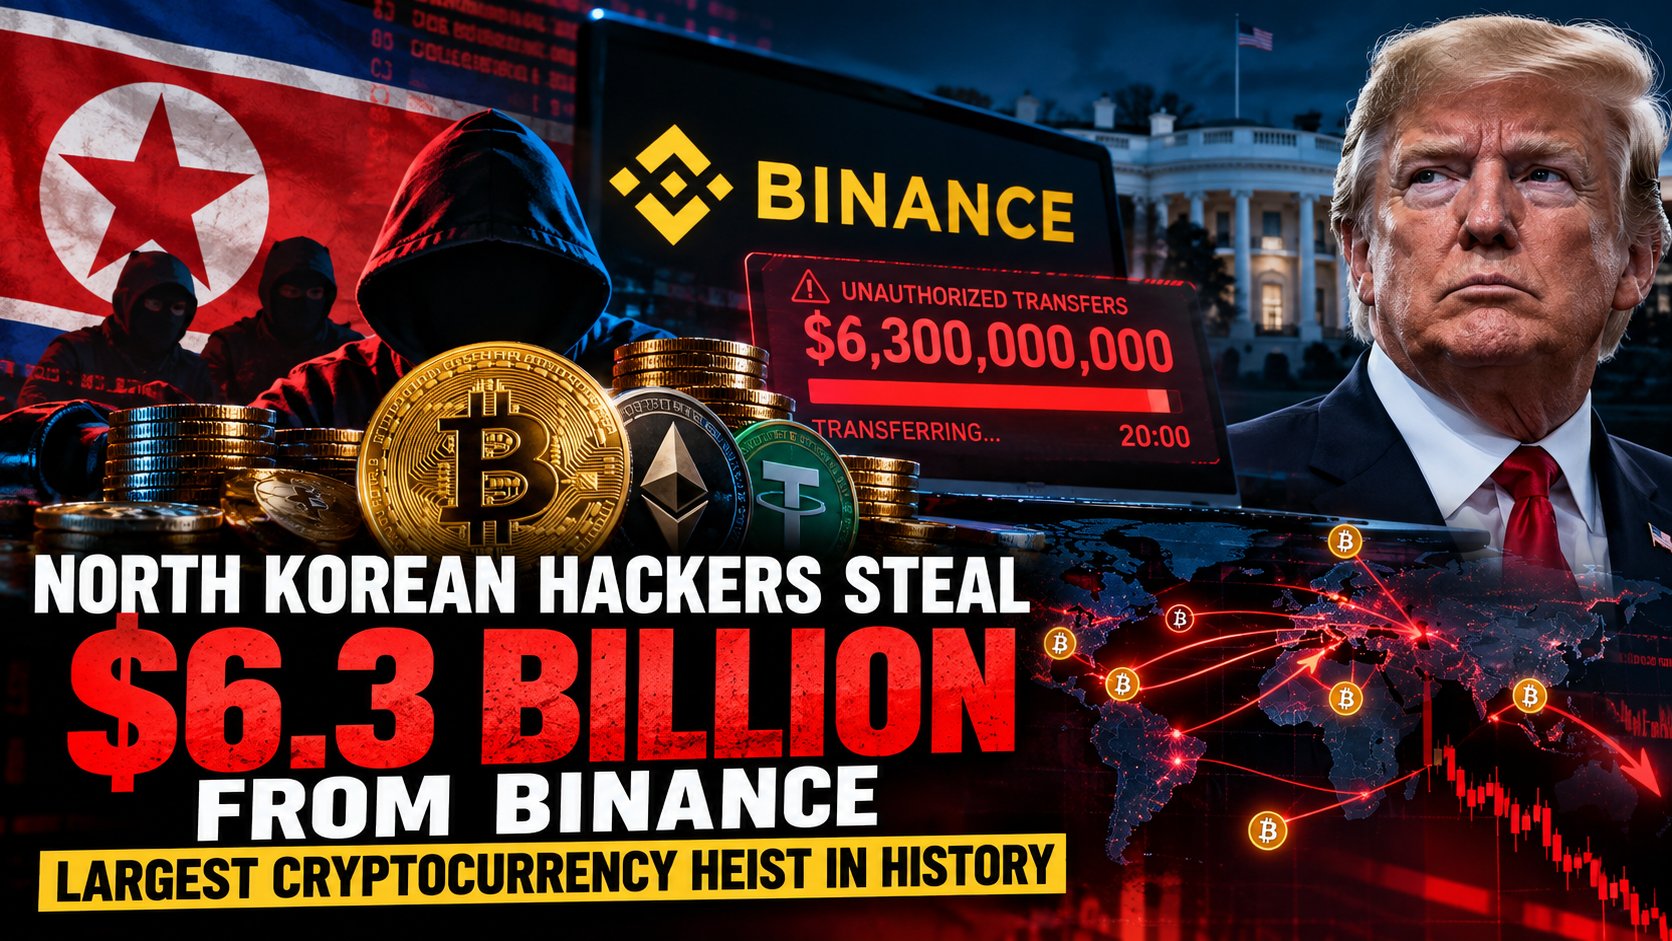
The largest cryptocurrency theft in history has exposed a massive security failure at the world’s biggest digital asset exchange, with blockchain investigators linking the unprecedented $6.3 billion attack to North Korea’s notorious state-sponsored hacking operation.
Hackers stole approximately $6.3 billion in digital assets from Binance on October 29, executing a highly coordinated cyberattack that moved most of the stolen cryptocurrency across 10 blockchain networks in approximately 20 minutes. The breach, which investigators believe involved compromised transaction authorization systems, represents the largest known cryptocurrency theft on record and raises serious questions about the security of the global digital asset industry.
American blockchain intelligence firm TRM Labs has attributed the attack to TraderTraitor, an elite North Korean hacking operation associated with the country’s broader state sponsored cybercrime apparatus. Chainalysis has also identified the group as the likely perpetrator, citing similarities to previous attacks, including the $1.5 billion theft from cryptocurrency exchange Bybit in February 2025. Although the evidence points toward North Korea, U.S. federal authorities have not publicly confirmed the identity of the attackers.
Binance has promised to absorb the entire financial impact of the breach rather than pass the losses on to customers. The company says approximately $3 billion in stolen assets has already been frozen through cooperation with cryptocurrency issuers, blockchain intelligence firms, and law enforcement agencies. However, billions more remain outside those freezes, creating a potentially enormous financial windfall for the attackers if they can successfully launder and convert the stolen cryptocurrency.
The incident has also drawn the attention of President Donald Trump, who acknowledged that American authorities were investigating the attack and its possible connection to North Korea. Beyond the immediate financial losses, the breach highlights a growing national security concern: sophisticated state backed hacking organizations can exploit weaknesses in cryptocurrency infrastructure to obtain billions of dollars while circumventing many of the safeguards that govern traditional financial institutions.
A $6.3 Billion Cryptocurrency Heist Executed in Just 20 Minutes
The attack began at approximately 4:05 p.m. Eastern Time on Thursday, October 29, when unauthorized transactions started transferring enormous quantities of cryptocurrency out of Binance controlled hot wallets. According to blockchain intelligence firm TRM Labs, the attackers moved approximately $6.36 billion across 10 separate blockchain networks, with the overwhelming majority of the assets transferred within a roughly 20 minute window.
The operation was remarkable not only for its size but also for its speed, precision, and coordination. Rather than attempting to exploit a single cryptocurrency network, the hackers targeted the infrastructure Binance uses to manage and authorize transactions across multiple digital asset ecosystems. The stolen assets included cryptocurrencies operating on major blockchain networks, demonstrating that the attack was directed at the exchange’s custody and transaction systems rather than an isolated vulnerability in Bitcoin, Ethereum, or another blockchain protocol.
Investigators have reported indications that the attackers prepared the operation in advance, including suspicious transaction activity preceding the large scale withdrawals. The rapid movement of funds suggests the perpetrators had established access and planned their transfers before initiating the main attack. By the time Binance identified the unauthorized activity and began implementing emergency security measures, billions of dollars had already been transferred to wallets outside the company’s control.
The scale of the theft dwarfs previous cryptocurrency breaches. In February 2025, hackers stole approximately $1.5 billion from Bybit, an incident that was then considered the largest cryptocurrency exchange theft in history. The Binance attack is more than four times that amount, setting a new benchmark for the financial damage that a sophisticated cyber operation can inflict on a digital asset company.
Unlike a conventional bank transfer, cryptocurrency transactions generally cannot be reversed after they have been confirmed on their respective blockchains. Investigators can trace the movement of stolen assets through public transaction records, but identifying where the money has gone does not automatically provide a mechanism for recovering it. That distinction has become central to the international effort to contain the damage from the Binance breach.
How Hackers Compromised Binance’s Security Systems
Binance initially reported that the attack may have originated with a compromised laptop belonging to a DevOps engineer, allowing unauthorized access to a service container involved in processing transactions. The exchange subsequently acknowledged that its investigation had uncovered additional points of compromise, indicating that the intrusion was more extensive than originally understood.
According to TRM Labs, the attackers compromised elements of Binance’s transaction signing infrastructure, the systems responsible for authorizing cryptocurrency transfers from wallets controlled by the exchange. This finding is particularly significant because cryptocurrency security depends not only on protecting private keys but also on securing the software, permissions, and operational systems authorized to initiate transactions.
In a conventional cryptocurrency theft, an attacker who obtains a wallet’s private key can potentially transfer its assets without the owner’s permission. However, an attacker who compromises an authorized signing service may be able to achieve a similar result without directly stealing the underlying private key. By manipulating trusted transaction authorization mechanisms, hackers can cause an exchange’s own infrastructure to approve transfers that appear technically valid to the blockchain network.
Binance has stated that investigators have found no evidence that its wallet private keys were leaked. That finding is consistent with the possibility that the attackers exploited weaknesses elsewhere in the authorization process, although the company has not yet published a complete technical explanation of the intrusion.
The exchange says it has contained the compromised infrastructure, revoked affected authorizations, strengthened security checks, and implemented additional controls intended to prevent further unauthorized withdrawals. Binance has also committed to publishing a detailed technical investigation once its findings have been verified.
The distinction between compromising a blockchain and compromising a cryptocurrency exchange is critical. Bitcoin and Ethereum can continue operating exactly as designed while a centralized company responsible for safeguarding customer assets suffers a catastrophic security failure. In this case, the apparent vulnerability was not the mathematical foundation of cryptocurrency itself, but the human operated technology responsible for managing billions of dollars in digital assets.
North Korea’s TraderTraitor Hacking Group Emerges as the Leading Suspect
Blockchain intelligence firm TRM Labs has identified TraderTraitor, a North Korean state sponsored hacking operation, as the likely organization responsible for the Binance theft. The company said its assessment was supported by both blockchain transaction analysis and intelligence collected outside the blockchain, describing its attribution as a high confidence finding.
TraderTraitor has been associated with North Korea’s broader Lazarus hacking ecosystem, a network of cyber operations linked by U.S. authorities to the country’s intelligence services. These groups have repeatedly targeted financial institutions, cryptocurrency exchanges, software developers, and technology companies, using sophisticated intrusions to steal digital assets and move them through complex laundering networks.
The Binance attack shares characteristics with earlier operations attributed to North Korean hackers, including the rapid movement of stolen funds, the exploitation of trusted transaction systems, and the use of multiple blockchain networks to complicate investigations. Chainalysis has independently identified TraderTraitor as the likely perpetrator, while other blockchain investigators have reported transaction patterns consistent with previous North Korean cryptocurrency thefts.
One of the most important comparisons involves the February 2025 Bybit breach. In that incident, hackers manipulated a cryptocurrency transaction authorization process, enabling the theft of approximately $1.5 billion in digital assets. The FBI subsequently attributed the operation to North Korean actors operating under the TraderTraitor designation.
The suspected connection between the two attacks suggests that North Korean cyber operations have become increasingly capable of targeting the infrastructure used by major cryptocurrency exchanges. Rather than relying exclusively on stolen passwords or conventional malware, these operations can exploit trusted employees, development environments, internal software services, and the transaction approval mechanisms that financial institutions depend upon.
However, blockchain intelligence assessments are not equivalent to formal government attribution. Transaction patterns, shared infrastructure, and laundering similarities can provide compelling evidence, but investigators must still establish which individuals and organizations controlled the relevant systems. As of October 30, the FBI had not publicly confirmed that North Korea carried out the Binance attack.
Binance Freezes $3 Billion, but Billions Remain Beyond Its Immediate Reach
One of the most significant developments following the breach has been the rapid freezing of approximately $3 billion in stolen cryptocurrency. Binance says it coordinated with stablecoin issuers, blockchain intelligence companies, other cryptocurrency businesses, and law enforcement agencies to identify affected assets and prevent further transfers.
A substantial portion of the frozen cryptocurrency consisted of stablecoins, including dollar pegged tokens such as USDT and USDC. Unlike Bitcoin, which operates without a central issuer, these assets are administered by companies that maintain certain controls over their tokens. Under appropriate circumstances, issuers can freeze balances associated with suspected criminal activity, preventing those particular tokens from being transferred.
Companies including Tether and Circle participated in the response, demonstrating how centralized controls within parts of the cryptocurrency ecosystem can help contain the damage from a major theft. Other industry participants also assisted in identifying and restricting affected assets as investigators attempted to follow the stolen funds across multiple networks.
However, the remaining billions present a much more complicated recovery challenge. Native cryptocurrencies such as Bitcoin and Ether generally cannot be frozen by a private company through an issuer controlled blacklist. Once those assets have been transferred into wallets controlled by the attackers, recovery may depend on obtaining control of the wallets, intercepting funds when they reach cooperating financial intermediaries, or identifying other legally and technically available means of seizure.
Investigators are also examining the movement of stolen cryptocurrency through decentralized finance platforms, where digital assets can be exchanged, deposited, or used as collateral for loans without passing through a conventional bank. Such transactions can create additional layers between the original theft and the assets ultimately controlled by the attackers.
Although approximately $3 billion has been frozen, that does not mean all of those assets have been returned to Binance. Likewise, the approximately $3.3 billion outside the reported freezes should not automatically be considered permanently lost. Some of those funds may remain traceable and potentially recoverable, but the prospects depend on the assets involved, the attackers’ subsequent transactions, and the cooperation of institutions that encounter the stolen cryptocurrency.
The recovery operation illustrates both the strengths and weaknesses of blockchain transparency. Investigators can often observe suspicious transactions in extraordinary detail, but the ability to follow stolen money across a public ledger does not necessarily provide the authority or technical means to retrieve it.
Binance Promises to Cover Customer Losses With More Than $6.34 Billion in Company Funds
Facing what may be the most serious security crisis in its history, Binance has announced that customers will not be required to absorb the financial losses associated with the attack. The company says it will use its corporate treasury and Secure Asset Fund for Users, commonly known as SAFU, to replace the stolen cryptocurrency.
In an October 30 security update, Binance confirmed that it had set aside more than $6.34 billion in company funds to address the incident. According to the exchange, approximately $5 billion in corresponding cryptocurrency assets had already been allocated toward replacing the stolen holdings, including Bitcoin, Ether, USDT, USDC, and BNB. Binance said it was purchasing additional assets through cryptocurrency markets and over-the-counter transactions to complete the replacement process.
The exchange has emphasized that the financial impact will be borne by the company rather than its customers. Nevertheless, its commitment to cover the losses remains distinct from actually recovering the stolen cryptocurrency. Even if Binance fully restores affected customer balances, the attackers could retain control of substantial amounts of stolen digital assets unless investigators successfully freeze or recover them.
As part of its emergency response, Binance temporarily suspended withdrawals while security teams examined affected systems, isolated compromised infrastructure, and implemented additional safeguards. The company said deposits and other unaffected services remained operational, while withdrawal services would be restored after the necessary security checks had been completed.
Binance also announced plans to publish updated proof-of-reserves information, allowing customers and market participants to evaluate the exchange’s asset holdings following the incident. Such disclosures may help establish whether the company has sufficient resources to meet its obligations, although reserve reporting alone cannot establish that every security vulnerability has been eliminated.
The company’s ability to cover the losses may prevent an immediate customer financial disaster, but it does not resolve the underlying security questions. Investors and regulators will still need to understand how an exchange managing enormous quantities of cryptocurrency allowed attackers to authorize transfers of this magnitude and whether comparable vulnerabilities exist elsewhere in the industry.
Trump Administration Investigates North Korean Connection as President Questions Cryptocurrency Security
The unprecedented theft has reached the White House, where President Donald Trump confirmed Friday that his administration was examining the breach and whether North Korean hackers were responsible. Speaking with reporters in the Oval Office, Trump acknowledged that federal authorities had not reached a definitive conclusion about the perpetrators, despite the growing evidence presented by private blockchain intelligence firms.
“We don’t know. We’re looking at that. We’re looking at that.” — President Donald Trump, October 30, 2026
The president also addressed Binance’s promise to cover the losses, noting that the exchange had expressed confidence in its ability to manage the financial consequences. However, Trump appeared less convinced about the underlying security of cryptocurrency transactions, contrasting digital assets with traditional methods of transferring money.
“You know the old fashioned way when you used to sign a check, take it out. These are different people. Never see the money anymore. So I’ve always felt it was a little bit dangerous.” — President Donald Trump
Trump’s comments highlight a growing challenge for an administration that has positioned itself as an advocate for the cryptocurrency industry. The White House has promoted digital asset development and a more favorable regulatory environment, but the Binance breach demonstrates that the industry’s expansion has also created opportunities for sophisticated criminal organizations and hostile foreign governments.
Reuters reported that the FBI and U.S. Secret Service were working with Binance following the attack, according to a person familiar with the investigation. American authorities are expected to examine both the technical aspects of the intrusion and the movement of stolen assets through international cryptocurrency networks. As of October 30, the administration had not publicly announced new sanctions or retaliatory measures specifically targeting North Korea over the incident.
The breach has also renewed debate over federal cryptocurrency regulation. Commodity Futures Trading Commission Chairman Michael Selig argued that offshore cryptocurrency exchanges lack some of the safeguards imposed on regulated American financial markets. Meanwhile, cryptocurrency industry representatives have urged Congress to establish clearer federal rules governing digital asset exchanges, custody requirements, and the authority to freeze suspicious transactions.
The political implications are particularly complicated because Trump pardoned Binance founder Changpeng Zhao in 2025, following Zhao’s earlier guilty plea involving failures to maintain an effective anti money laundering program. That previous criminal case is separate from the October 2026 cyberattack, and there is no evidence establishing a connection between Zhao’s earlier violations and the latest breach. Nevertheless, the exchange’s history and the administration’s cryptocurrency policies are likely to become part of the broader debate over financial oversight and consumer protection.
North Korea Has Turned Cryptocurrency Theft Into a National Security Threat
The suspected involvement of North Korea transforms the Binance breach from an extraordinary financial crime into a potentially serious international security issue. For years, American intelligence agencies, international investigators, and United Nations experts have warned that North Korean cyber operations target cryptocurrency businesses and financial institutions to obtain revenue for a government constrained by international sanctions.
North Korea’s hacking operations differ from ordinary cybercriminal enterprises because investigators believe at least some of the proceeds support state priorities, including prohibited nuclear weapons and ballistic missile programs. The country’s ability to generate revenue through cybercrime has become particularly concerning as conventional sanctions restrict its access to international banking networks, trade financing, and foreign currency.
Cryptocurrency presents an attractive target because enormous amounts of value can be transferred across international borders without relying on the traditional correspondent banking system. Although blockchain transactions are often publicly visible, criminals can complicate investigations by moving assets between wallets, exchanging cryptocurrencies, using decentralized finance platforms, and attempting to convert stolen tokens through intermediaries operating in different jurisdictions.
The February 2025 Bybit attack demonstrated the scale of this threat when North Korean hackers stole approximately $1.5 billion in digital assets. The FBI attributed that operation to TraderTraitor, identifying the group as part of a broader campaign of cryptocurrency theft and money laundering. If investigators ultimately confirm that the same organization carried out the Binance attack, it would represent a dramatic escalation in the financial capabilities of North Korea’s state sponsored hacking apparatus.
The national security implications extend beyond the immediate loss suffered by Binance. A successful multibillion dollar theft could potentially provide North Korea with access to resources that would otherwise be difficult to obtain through legitimate international commerce. However, the full value of the stolen cryptocurrency cannot automatically be treated as money available to the North Korean government. Assets that have been frozen, remain traceable, or cannot be successfully converted into usable funds may never produce an equivalent financial benefit for the perpetrators.
That distinction will become increasingly important as investigators attempt to determine how much of the stolen cryptocurrency can be recovered and how much may ultimately disappear into laundering networks. Even partial success by the attackers could produce an extraordinary financial return, reinforcing concerns that cybercrime has become a strategic source of revenue for sanctioned governments.
Cryptocurrency Markets React as Investors Question Exchange Security
The Binance attack triggered immediate turbulence across cryptocurrency markets, with Bitcoin and Ether declining as investors absorbed news of the record breaking theft. Bitcoin traded below $80,000 during Friday’s market reaction, while shares of publicly traded cryptocurrency related companies also came under pressure. Coinbase, Strategy, and other businesses connected to the digital asset industry experienced selling as investors reassessed the potential consequences of the breach.
The market response reflected concerns extending beyond Binance’s immediate financial position. As the world’s largest cryptocurrency exchange by trading volume, Binance occupies a central role in the digital asset ecosystem, providing trading, custody, and liquidity services to customers around the world. A security failure involving billions of dollars raises questions about whether other major exchanges rely on similarly vulnerable transaction authorization systems.
The incident also illustrates the risks associated with centralized cryptocurrency custody. Although digital assets are frequently promoted as an alternative to traditional financial intermediaries, many investors do not hold their cryptocurrency directly. Instead, they deposit assets with exchanges that manage the private keys, transaction infrastructure, and operational security necessary to process withdrawals and trading activity.
These arrangements create concentrated pools of digital wealth that can become extraordinarily attractive targets for sophisticated hackers. Exchanges generally attempt to reduce that exposure by maintaining portions of their reserves in offline cold storage while using internet-connected hot wallets to process routine transactions. However, a compromised hot wallet or its associated authorization systems can still expose enormous quantities of cryptocurrency if sufficient safeguards are not in place.
Unlike eligible deposits held at FDIC insured American banks, cryptocurrency balances maintained on exchanges generally do not receive federal deposit insurance protection. Binance’s promise to reimburse customers is therefore a corporate commitment rather than a government-backed guarantee. Customers of other exchanges cannot assume they would receive the same financial protection following a comparable attack.
For investors, the Binance breach raises an uncomfortable question about the relationship between convenience and control. Cryptocurrency exchanges simplify digital asset ownership, but customers who entrust those assets to a third party also become dependent on that company’s security practices, financial reserves, and ability to respond to emergencies.
The Binance Attack Exposes a Fundamental Weakness in Cryptocurrency’s Financial Infrastructure
The most troubling aspect of the Binance breach may not be the staggering amount stolen, but the apparent failure of security systems specifically designed to prevent unauthorized access to enormous holdings of digital assets. The attackers did not need to undermine the mathematical foundations of Bitcoin or Ethereum. Instead, investigators believe they exploited the operational infrastructure responsible for authorizing transfers from one of the world’s most important cryptocurrency businesses.
That distinction challenges one of the central narratives surrounding digital assets. Cryptocurrency advocates frequently emphasize the security, transparency, and decentralization of blockchain networks, but those characteristics do not automatically protect investors from vulnerabilities introduced by centralized exchanges, compromised employees, software infrastructure, or inadequate transaction approval controls.
The Binance attack demonstrates how the security of a financial system can depend on its weakest operational component, regardless of how sophisticated the underlying technology may be. A blockchain transaction can be cryptographically valid while still representing an unauthorized theft if the systems responsible for approving it have been compromised.
Investigators must now establish how the attackers gained access, which security controls failed, whether the breach involved additional compromised infrastructure, and why suspicious transfers were not stopped before billions of dollars left the exchange. Binance’s forthcoming technical report will be essential to answering those questions, although an independent examination may ultimately be necessary to establish the full scope of the failure.
The incident also raises important regulatory questions. Financial institutions entrusted with billions of dollars in customer assets are expected to maintain rigorous safeguards, independent oversight, and operational controls. Cryptocurrency exchanges operate under a patchwork of international regulations, creating significant differences in how customer funds are protected and how companies are required to demonstrate the effectiveness of their cybersecurity programs.
Stronger transaction approval procedures, independent security audits, limits on hot wallet exposure, improved employee access controls, and more transparent reserve reporting could reduce some of these risks. However, no single regulatory framework or technical safeguard can eliminate the possibility of a sophisticated cyberattack, particularly when the suspected adversary has the resources and experience of a state-sponsored hacking organization.
The central challenge is determining how to preserve the advantages of cryptocurrency technology without allowing enormous concentrations of digital wealth to remain vulnerable to catastrophic operational failures.
The World’s Largest Crypto Heist Could Have Consequences Far Beyond Binance
Binance’s commitment to cover the stolen assets may prevent the immediate financial losses from falling on customers, but it cannot erase the broader implications of the attack. A suspected North Korean hacking operation has demonstrated the ability to penetrate a major cryptocurrency exchange and move more than $6 billion across international blockchain networks in a matter of minutes.
For Binance, the coming days will be critical as the company works to restore normal withdrawal services, replenish affected assets, publish updated reserve information, and explain how its security infrastructure was compromised. For law enforcement, the priority will be identifying the perpetrators, tracing the stolen cryptocurrency, and preventing as much of the money as possible from reaching criminal or sanctioned organizations.
For the Trump administration, the incident presents a difficult policy challenge. Washington has encouraged cryptocurrency innovation and positioned the United States as a potential global leader in digital assets, yet the Binance breach underscores the national security risks that can emerge when financial technology develops faster than the systems designed to protect it.
The theft also creates an uncomfortable reality for an industry that has spent years promoting cryptocurrency as a safer, faster, and more transparent alternative to conventional finance. The blockchain networks involved may have functioned as intended, but the centralized infrastructure connecting customers to those networks appears to have failed on an extraordinary scale.
Ultimately, the Binance attack is about more than a single exchange, a group of hackers, or the recovery of stolen cryptocurrency. It is about whether a rapidly expanding financial system can provide the security, accountability, and consumer protections necessary to justify the enormous sums of money entrusted to it. If investigators confirm that North Korea was responsible, the world will be confronting a new milestone in state sponsored financial cybercrime: a single operation capable of moving more than $6 billion beyond a major financial institution’s control in approximately 20 minutes. Binance may have the financial resources to reimburse its customers, but the global cryptocurrency industry still faces a far more difficult task: proving that the next attack can be prevented.
Sources & Further Reading
Official Statements and Primary Sources
Independent Reporting and Cybersecurity Analysis
SFL Media Related Coverage













Want to join the conversation?
Create an account or sign in to share your thoughts, vote,
and reply to other readers.
Showing 0 of 0 comments
Don't have an account?
Already have an account?